There are 8 steps to managing your network's security including: Be Organized. Develop and enforce a strong password policy. Ensure firewalls are properly configured. It implements security measures, policies, and tools that safeguard the entire network infrastructure to achieve the goal. This framework establishes best practices for device authentication, firmware updates, and real-time monitoring to detect potential threats. Develop data. This Security Requirements Guide (SRG) is published as a tool to improve the security of Department of Defense (DOD) information systems.
Low-voltage wiring, used in security cameras and internet networks, must follow specific safety rules to ensure it is installed correctly and safely. These rules are mainly outlined in the National Electrical Code (N.
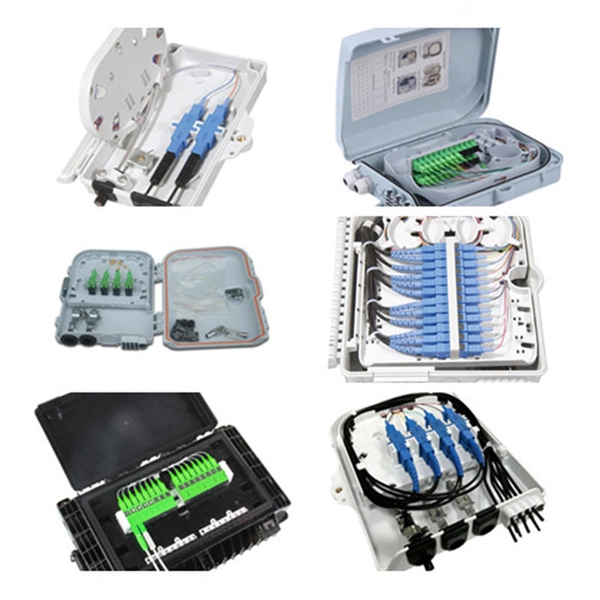
Key measures include securing network terminals, data centers, and access points with controlled entry systems, surveillance cameras, and fencing. Regular inspections and tamper-evident seals on fiber enclosures help detect unauthorized access or accidental damage early. Nowadays, the increasing reliance on fiber optic networks for transmitting vast amounts of data has brought about a pressing need for robust security measures to counter potential threats. In this fast-paced digital landscape, organizations must adopt a comprehensive approach to safeguarding their. In this blog, we will take an in-depth look at security measures for fiber optic communications, examining different strategies and technologies to ensure that data transmitted over this advanced infrastructure is intact and confidential. However, fiber is not invulnerable. Attackers with specialized tools can: Physically access unsecured junctions or cabinets.
[PDF Version]
This section provides an overview of SIP trunk encryption, gateway encryptions and security profile setup tips. SIP trunks can support secure calls both for signaling as well as media; TLS provides signaling encryption and SRTP provides media encryption. SIP Gateway lets your organization use any compatible SIP device with Microsoft Teams to preserve your investments in SIP devices. Compatible devices can be Skype for Business IP. SIP is a text-based protocol modeled on the structure of HTTP and SMTP, enabling interoperability and integration with other Internet applications. From the Device Security Mode drop-down. To benefit from the latest communication and collaboration solutions, businesses are increasingly turning to Session Initiation Protocol (SIP) based networks. SIP is a widely adopted standard in the telecommunications industry, and it provides increased flexibility for inter-connectivity and everyday use.
[PDF Version]
Network security audits help protect sensitive data by evaluating access controls, identifying security weaknesses such as open ports or outdated software, monitoring unauthorized activity, and ensuring compliance with data protection regulations such as GDPR or PCI DSS. This blog is about the top 10 network security testing methodologies that every cybersecurity professional should adopt in 2025. By learning and implementing these, organizations can strengthen their defenses and stay safe from attackers. The sophistication level of cyberattacks is staggering. public companies must disclose any cybersecurity incident they determine to be 'material' within four business days of that determination. Meanwhile, the average. Regular testing, integration with DevOps/CloudOps, combining automation with human expertise, and partnering with experts like Zymr, ensure enterprises stay resilient against evolving AI-driven and cloud-focused threats. Critical areas to focus on include evaluating firewalls, access controls, encryption methods, network segmentation, and patch management.
[PDF Version]
You'll get the precise, standardized dimensions of a 1U server rack unit — including height (1. 45 mm), width (19″ / 48. 26 cm), mounting hole spacing, and critical clearance allowances — plus actionable guidance on verifying physical fit, avoiding common installation. The IPC-C1E-BAR30-RH-N1 is an entry-level 1U appliance chassis with 15” depth for space-sensitive applications, such as Network & Security appliance, firewall, VPN, Telephony and military applications. 6” x 12”) motherboard can be populated into this appliance chassis. reserves the right to make any final modifications. For example, a typical full-size rack cage is 42U high, while equipment is typically 1U, 2U, 3U, or 4U high.
You can create, filter, modify, or delete IPS signatures on the IPS Policy Signatures page in Security Director. The intrusion prevention system (IPS) compares traffic against signatures of known threats and blocks traffic when a threat is detected. To detect such activity, IPS uses signatures. government repository of standards based vulnerability management data represented using the Security Content Automation Protocol (SCAP). The NVD includes databases of security. Many firewall manufacturers can provide the IDS / IPS module with an additional license in their products. Snort can be deployed inline to stop these. These databases store unique threat signatures,malware patterns, virus definitions, intrusion fingerprints,that security tools rely on to spot malicious activity.
Contact us for competitive quotes on any of our power communication and smart grid products
Get a Quote