, officially the Republic of Sierra Leone, is a country in. The is that of a with a of approximately US$1.9 billion in 2009. Since the end of the civil war in 2002 the economy is gradually recovering with a GDP growth rate between 4 and 7%. In 2008 its GDP in ranked between 147th (World Bank) and 153rd (CIA) largest in the w.
Recognizing the critical need to curb fire disasters, the NDMA has launched a comprehensive action plan focused on prevention, preparedness, and response. The Agency is implementing the following key interventions: Coordinating with the National Fire Force to improve. The National Disaster Management Agency (NDMA) has recorded a concerning rise in fire-related disasters, with 67 out of 71 incidents recorded in the first quarter of 2025 caused by fire outbreaks. This staggering 94% of all reported disasters emphasises the urgent need for stronger fire prevention. The Sierra Leone Fire Force has warned citizens to be careful with fire outbreak, citing likelihood of an increase in fire disasters in the country.
In this comprehensive guide, we'll walk you through each stage of the process, from understanding why business owners decide to sell, to preparing your company for the market, determining its value, finding qualified buyers, and managing negotiations through to closing. Selling your security systems installation business is a major decision, and knowing where to start can be challenging. Businesses often encounter challenges in handling excess technology, especially when it comes to pre-owned networking devices. Implementing best practices ensures that these devices are sold. Enterprises replacing networking hardware end up with surplus devices, including routers, switches, firewalls, and storage units. Holding onto these assets can occupy valuable space and tie up resources that could be better deployed. What you need is a network equipment.
The EU EN 18031 certification introduces a new era of cybersecurity compliance under the Radio Equipment Directive (RED). This article. Network devices represent one of the core pillars of IoT, enabling the smart “things” to connect and communicate with each other. The standard is highly technical, divided into three detailed parts, and can be challenging to navigate without. From the CCDB established Working Group, the Network Device International Technical Community (ND-iTC) was formed. Since August 1, 2025, these requirements have been in full force.
This document provides the overall architecture for Deterministic Networking (DetNet), which provides a capability to carry specified unicast or multicast data flows for real-time applications with extremely low data loss rates and bounded latency within a network domain. ● Other distribution automation applications such as Direct Transfer Trip. Our engineers are experts at multifunction microprocessor-based relay technology, and we design protection schemes for generation, transmission, distribution, and low-volt ge systems worldwide. Of particular concern is the potential for cyberattacks that exploit high-wattage IoT devices, such as EV chargers, to manipulate local demand and destabilize the grid. With tools ranging from intent-based networking to policy-driven orchestration and multi-cloud integration, these leading. The handbook describes various power distribution system constructions and elements there-of, technical considerations, distribution automation infrastructure and functionality, communication aspects, special automation applications and life cycle aspects.
[PDF Version]
The Logs section provides the tools to view the system logs, authentication logs and auditing logs as well as download the logs in CSV format. Firewall logs can be used by the administrator for troubleshooting network. You can access the system logs by. A security information and event management (SIEM) solution ensures a healthy security posture for an organization's network by monitoring different types of data from the network. Think of logs as breadcrumbs that show everything happening across your routers, switches, firewalls, and other network infrastructure. This includes considerations for configuring the logging settings for different policies, the configuration of local log storage databases, and setting both local logging for the Firewall. A log is an automatically generated, time-stamped file that provides an audit trail for system events on the firewall or network traffic events that the firewall monitors. In this comprehensive guide, we will cover the key concepts, tools, and techniques for analyzing log. Alternate format: Network security logging and monitoring - ITSAP.
[PDF Version]
You can create, filter, modify, or delete IPS signatures on the IPS Policy Signatures page in Security Director. The intrusion prevention system (IPS) compares traffic against signatures of known threats and blocks traffic when a threat is detected. To detect such activity, IPS uses signatures. government repository of standards based vulnerability management data represented using the Security Content Automation Protocol (SCAP). The NVD includes databases of security. Many firewall manufacturers can provide the IDS / IPS module with an additional license in their products. Snort can be deployed inline to stop these. These databases store unique threat signatures,malware patterns, virus definitions, intrusion fingerprints,that security tools rely on to spot malicious activity.
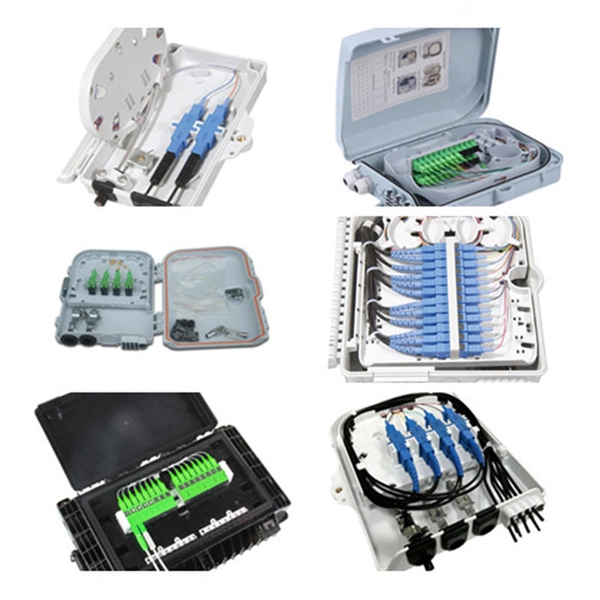
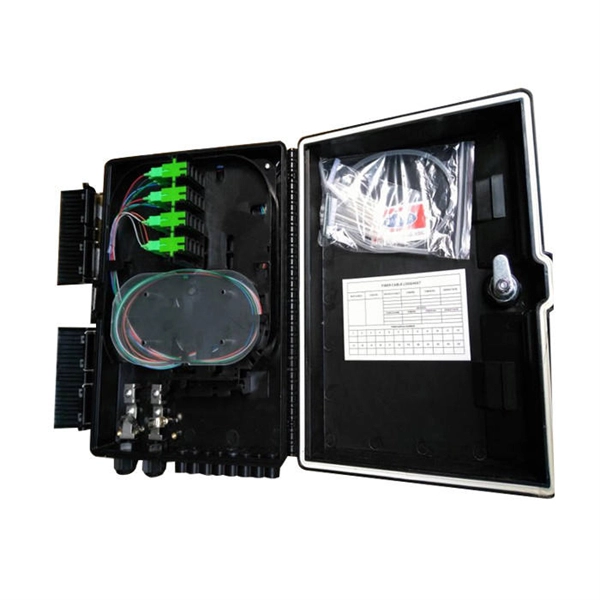
Key measures include securing network terminals, data centers, and access points with controlled entry systems, surveillance cameras, and fencing. Regular inspections and tamper-evident seals on fiber enclosures help detect unauthorized access or accidental damage early. Nowadays, the increasing reliance on fiber optic networks for transmitting vast amounts of data has brought about a pressing need for robust security measures to counter potential threats. In this fast-paced digital landscape, organizations must adopt a comprehensive approach to safeguarding their. In this blog, we will take an in-depth look at security measures for fiber optic communications, examining different strategies and technologies to ensure that data transmitted over this advanced infrastructure is intact and confidential. However, fiber is not invulnerable. Attackers with specialized tools can: Physically access unsecured junctions or cabinets.
[PDF Version]Contact us for competitive quotes on any of our power communication and smart grid products
Get a Quote