This document provides the overall architecture for Deterministic Networking (DetNet), which provides a capability to carry specified unicast or multicast data flows for real-time applications with extremely low data loss rates and bounded latency within a network domain. ● Other distribution automation applications such as Direct Transfer Trip. Our engineers are experts at multifunction microprocessor-based relay technology, and we design protection schemes for generation, transmission, distribution, and low-volt ge systems worldwide. Of particular concern is the potential for cyberattacks that exploit high-wattage IoT devices, such as EV chargers, to manipulate local demand and destabilize the grid. With tools ranging from intent-based networking to policy-driven orchestration and multi-cloud integration, these leading. The handbook describes various power distribution system constructions and elements there-of, technical considerations, distribution automation infrastructure and functionality, communication aspects, special automation applications and life cycle aspects.
[PDF Version]
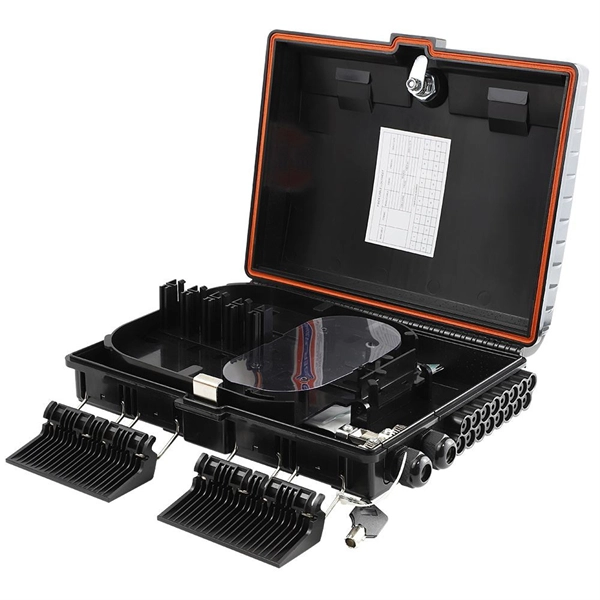
Key measures include securing network terminals, data centers, and access points with controlled entry systems, surveillance cameras, and fencing. Regular inspections and tamper-evident seals on fiber enclosures help detect unauthorized access or accidental damage early. Nowadays, the increasing reliance on fiber optic networks for transmitting vast amounts of data has brought about a pressing need for robust security measures to counter potential threats. In this fast-paced digital landscape, organizations must adopt a comprehensive approach to safeguarding their. In this blog, we will take an in-depth look at security measures for fiber optic communications, examining different strategies and technologies to ensure that data transmitted over this advanced infrastructure is intact and confidential. However, fiber is not invulnerable. Attackers with specialized tools can: Physically access unsecured junctions or cabinets.
[PDF Version]
The best splicers offer core alignment, fast splice times, durable designs, and smart features like cloud syncing and automated calibration. Top-rated models. A fusion splicer is the most expensive tool in a fiber tech's kit and the one you rely on most. This guide compares the key specs that matter in the field and helps you match the right splicer to your workload.
This section provides an overview of SIP trunk encryption, gateway encryptions and security profile setup tips. SIP trunks can support secure calls both for signaling as well as media; TLS provides signaling encryption and SRTP provides media encryption. SIP Gateway lets your organization use any compatible SIP device with Microsoft Teams to preserve your investments in SIP devices. Compatible devices can be Skype for Business IP. SIP is a text-based protocol modeled on the structure of HTTP and SMTP, enabling interoperability and integration with other Internet applications. From the Device Security Mode drop-down. To benefit from the latest communication and collaboration solutions, businesses are increasingly turning to Session Initiation Protocol (SIP) based networks. SIP is a widely adopted standard in the telecommunications industry, and it provides increased flexibility for inter-connectivity and everyday use.
[PDF Version]
There are 8 steps to managing your network's security including: Be Organized. Develop and enforce a strong password policy. Ensure firewalls are properly configured. It implements security measures, policies, and tools that safeguard the entire network infrastructure to achieve the goal. This framework establishes best practices for device authentication, firmware updates, and real-time monitoring to detect potential threats. Develop data. This Security Requirements Guide (SRG) is published as a tool to improve the security of Department of Defense (DOD) information systems.
In this comprehensive guide, we'll walk you through each stage of the process, from understanding why business owners decide to sell, to preparing your company for the market, determining its value, finding qualified buyers, and managing negotiations through to closing. Selling your security systems installation business is a major decision, and knowing where to start can be challenging. Businesses often encounter challenges in handling excess technology, especially when it comes to pre-owned networking devices. Implementing best practices ensures that these devices are sold. Enterprises replacing networking hardware end up with surplus devices, including routers, switches, firewalls, and storage units. Holding onto these assets can occupy valuable space and tie up resources that could be better deployed. What you need is a network equipment.
Our hybrid powered cable transmits data and power in one cable, ideal for powering security cameras, Wi-Fi access points, and more, eliminating the need for separate data and power lines. Uninterrupted monitoring of large infrastructure for increased safety and targeted preventative maintenance. Various cable constructions within the portfolio offer unlimited. CommScope bundles hybrid cabling to your custom specifications, using our high-performance fiber-optic, unshielded twisted pair and coaxial cables. ActiFi is a Class 3‑rated composite cable that supports low‑voltage (Class 2, 57 VDC/100 V) as well as bulk power solutions.
Network security audits help protect sensitive data by evaluating access controls, identifying security weaknesses such as open ports or outdated software, monitoring unauthorized activity, and ensuring compliance with data protection regulations such as GDPR or PCI DSS. This blog is about the top 10 network security testing methodologies that every cybersecurity professional should adopt in 2025. By learning and implementing these, organizations can strengthen their defenses and stay safe from attackers. The sophistication level of cyberattacks is staggering. public companies must disclose any cybersecurity incident they determine to be 'material' within four business days of that determination. Meanwhile, the average. Regular testing, integration with DevOps/CloudOps, combining automation with human expertise, and partnering with experts like Zymr, ensure enterprises stay resilient against evolving AI-driven and cloud-focused threats. Critical areas to focus on include evaluating firewalls, access controls, encryption methods, network segmentation, and patch management.
[PDF Version]Contact us for competitive quotes on any of our power communication and smart grid products
Get a Quote