Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. This guide evaluates the 10 best network security solutions for 2026, detailing technical specifications, key strengths, purchase rationale, and unique capabilities for global enterprises, mid-market growth companies, and hybrid workforces.
You can create, filter, modify, or delete IPS signatures on the IPS Policy Signatures page in Security Director. The intrusion prevention system (IPS) compares traffic against signatures of known threats and blocks traffic when a threat is detected. To detect such activity, IPS uses signatures. government repository of standards based vulnerability management data represented using the Security Content Automation Protocol (SCAP). The NVD includes databases of security. Many firewall manufacturers can provide the IDS / IPS module with an additional license in their products. Snort can be deployed inline to stop these. These databases store unique threat signatures,malware patterns, virus definitions, intrusion fingerprints,that security tools rely on to spot malicious activity.
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. Effective security systems have multiple layers, like an onion.
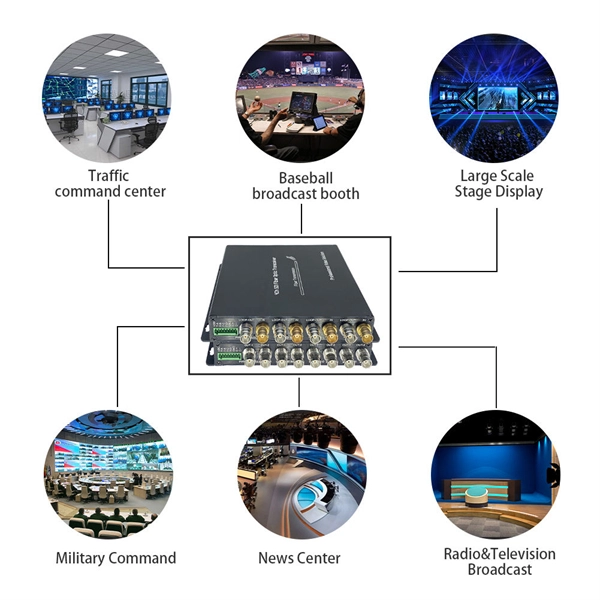
You'll get the precise, standardized dimensions of a 1U server rack unit — including height (1. 45 mm), width (19″ / 48. 26 cm), mounting hole spacing, and critical clearance allowances — plus actionable guidance on verifying physical fit, avoiding common installation. The IPC-C1E-BAR30-RH-N1 is an entry-level 1U appliance chassis with 15” depth for space-sensitive applications, such as Network & Security appliance, firewall, VPN, Telephony and military applications. 6” x 12”) motherboard can be populated into this appliance chassis. reserves the right to make any final modifications. For example, a typical full-size rack cage is 42U high, while equipment is typically 1U, 2U, 3U, or 4U high.
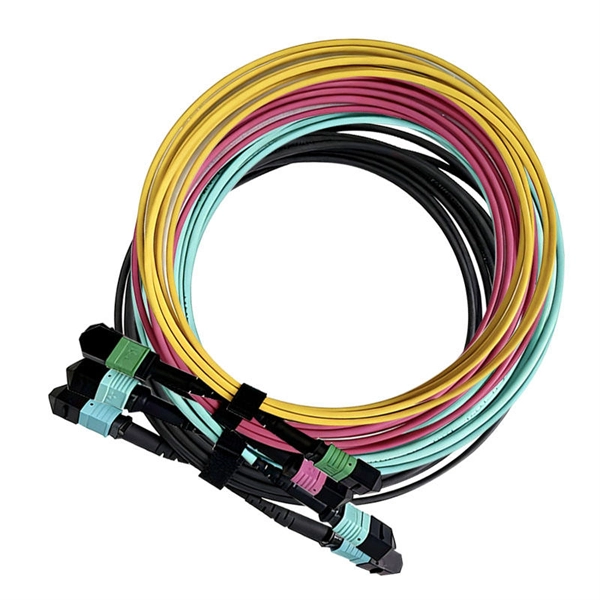
Our hybrid powered cable transmits data and power in one cable, ideal for powering security cameras, Wi-Fi access points, and more, eliminating the need for separate data and power lines. Uninterrupted monitoring of large infrastructure for increased safety and targeted preventative maintenance. Various cable constructions within the portfolio offer unlimited. CommScope bundles hybrid cabling to your custom specifications, using our high-performance fiber-optic, unshielded twisted pair and coaxial cables. ActiFi is a Class 3‑rated composite cable that supports low‑voltage (Class 2, 57 VDC/100 V) as well as bulk power solutions.
The National Authority for Cybersecurity received new advanced equipment to protect its network. This support strengthens Albania's cyber capacities. It marked an. Under the deal, Presight AI, a part of the G42 Group, will install surveillance cameras throughout Tirana and other major Albanian cities, as well as establish command and control centres. In a response to a Freedom of Information Act request, the Albanian Interior Ministry reported that the Smart. With the approval of Law No.
Network security audits help protect sensitive data by evaluating access controls, identifying security weaknesses such as open ports or outdated software, monitoring unauthorized activity, and ensuring compliance with data protection regulations such as GDPR or PCI DSS. This blog is about the top 10 network security testing methodologies that every cybersecurity professional should adopt in 2025. By learning and implementing these, organizations can strengthen their defenses and stay safe from attackers. The sophistication level of cyberattacks is staggering. public companies must disclose any cybersecurity incident they determine to be 'material' within four business days of that determination. Meanwhile, the average. Regular testing, integration with DevOps/CloudOps, combining automation with human expertise, and partnering with experts like Zymr, ensure enterprises stay resilient against evolving AI-driven and cloud-focused threats. Critical areas to focus on include evaluating firewalls, access controls, encryption methods, network segmentation, and patch management.
[PDF Version]
The Logs section provides the tools to view the system logs, authentication logs and auditing logs as well as download the logs in CSV format. Firewall logs can be used by the administrator for troubleshooting network. You can access the system logs by. A security information and event management (SIEM) solution ensures a healthy security posture for an organization's network by monitoring different types of data from the network. Think of logs as breadcrumbs that show everything happening across your routers, switches, firewalls, and other network infrastructure. This includes considerations for configuring the logging settings for different policies, the configuration of local log storage databases, and setting both local logging for the Firewall. A log is an automatically generated, time-stamped file that provides an audit trail for system events on the firewall or network traffic events that the firewall monitors. In this comprehensive guide, we will cover the key concepts, tools, and techniques for analyzing log. Alternate format: Network security logging and monitoring - ITSAP.
[PDF Version]
This section provides an overview of SIP trunk encryption, gateway encryptions and security profile setup tips. SIP trunks can support secure calls both for signaling as well as media; TLS provides signaling encryption and SRTP provides media encryption. SIP Gateway lets your organization use any compatible SIP device with Microsoft Teams to preserve your investments in SIP devices. Compatible devices can be Skype for Business IP. SIP is a text-based protocol modeled on the structure of HTTP and SMTP, enabling interoperability and integration with other Internet applications. From the Device Security Mode drop-down. To benefit from the latest communication and collaboration solutions, businesses are increasingly turning to Session Initiation Protocol (SIP) based networks. SIP is a widely adopted standard in the telecommunications industry, and it provides increased flexibility for inter-connectivity and everyday use.
[PDF Version]
This document provides the overall architecture for Deterministic Networking (DetNet), which provides a capability to carry specified unicast or multicast data flows for real-time applications with extremely low data loss rates and bounded latency within a network domain. ● Other distribution automation applications such as Direct Transfer Trip. Our engineers are experts at multifunction microprocessor-based relay technology, and we design protection schemes for generation, transmission, distribution, and low-volt ge systems worldwide. Of particular concern is the potential for cyberattacks that exploit high-wattage IoT devices, such as EV chargers, to manipulate local demand and destabilize the grid. With tools ranging from intent-based networking to policy-driven orchestration and multi-cloud integration, these leading. The handbook describes various power distribution system constructions and elements there-of, technical considerations, distribution automation infrastructure and functionality, communication aspects, special automation applications and life cycle aspects.
[PDF Version]Contact us for competitive quotes on any of our power communication and smart grid products
Get a Quote