
ODN Class A, B, and C are differentiated mainly on the optical transmitter power output and bit-rate optical receiver sensitivity. An optical module is a typically hot-pluggable optical transceiver used in high-bandwidth data communications applications. Optical modules typically have an electrical interface on the side that connects to the inside of the system and an optical interface on the side that connects to the outside. A GPON optical module is a transceiver used in GPON networks to convert electrical signals into optical signals and vice versa. This bidirectional module, equipped with an SC receptacle, operates over simplex single-mode fiber optic cables. Operating at the physical layer of the OSI model, optical modules are core devices in optical. The differences between optical fiber grades A, B, C, and D primarily pertain to the quality of the fiber end-face, which significantly impacts performance metrics such as insertion loss (IL) and return loss (RL). These grades are defined by standards that specify acceptable tolerances for various.
[PDF Version]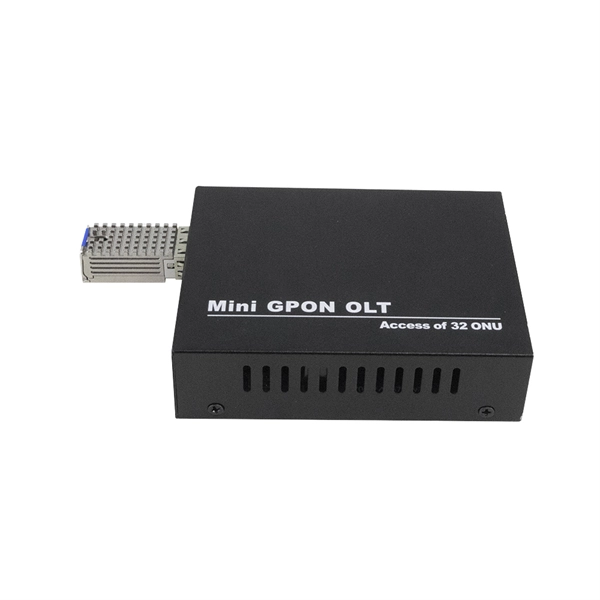
You can create, filter, modify, or delete IPS signatures on the IPS Policy Signatures page in Security Director. The intrusion prevention system (IPS) compares traffic against signatures of known threats and blocks traffic when a threat is detected. To detect such activity, IPS uses signatures. government repository of standards based vulnerability management data represented using the Security Content Automation Protocol (SCAP). The NVD includes databases of security. Many firewall manufacturers can provide the IDS / IPS module with an additional license in their products. Snort can be deployed inline to stop these. These databases store unique threat signatures,malware patterns, virus definitions, intrusion fingerprints,that security tools rely on to spot malicious activity.
The Logs section provides the tools to view the system logs, authentication logs and auditing logs as well as download the logs in CSV format. Firewall logs can be used by the administrator for troubleshooting network. You can access the system logs by. A security information and event management (SIEM) solution ensures a healthy security posture for an organization's network by monitoring different types of data from the network. Think of logs as breadcrumbs that show everything happening across your routers, switches, firewalls, and other network infrastructure. This includes considerations for configuring the logging settings for different policies, the configuration of local log storage databases, and setting both local logging for the Firewall. A log is an automatically generated, time-stamped file that provides an audit trail for system events on the firewall or network traffic events that the firewall monitors. In this comprehensive guide, we will cover the key concepts, tools, and techniques for analyzing log. Alternate format: Network security logging and monitoring - ITSAP.
[PDF Version]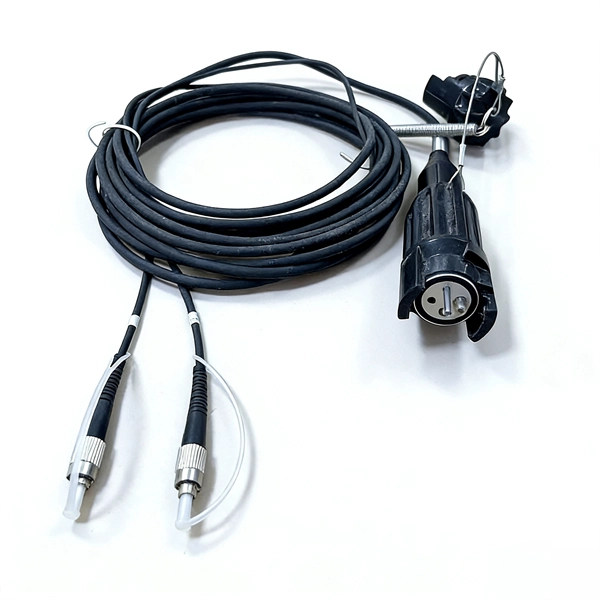
They power essential devices like security cameras, access points, and VoIP phones without the need for extra wiring. Rather than utilizing a wireless network that can be hacked through any number of online devices, PoE transmits data via one cable that cannot be attacked unless there is a direct, wired connection. It eliminates the need for separate power supplies, thus helping to streamline installation and reduce clutter. With this, PoE offers more flexibility. I've researched the top PoE network switches of 2025 and found excellent options for different needs, from compact unmanaged models to powerful managed switches with high PoE budgets. If you're looking for a. If you're building or upgrading a video surveillance network, one of the most important components to get right is your PoE (Power over Ethernet) switch. It compares PoE with WiFi and.
Network security audits help protect sensitive data by evaluating access controls, identifying security weaknesses such as open ports or outdated software, monitoring unauthorized activity, and ensuring compliance with data protection regulations such as GDPR or PCI DSS. This blog is about the top 10 network security testing methodologies that every cybersecurity professional should adopt in 2025. By learning and implementing these, organizations can strengthen their defenses and stay safe from attackers. The sophistication level of cyberattacks is staggering. public companies must disclose any cybersecurity incident they determine to be 'material' within four business days of that determination. Meanwhile, the average. Regular testing, integration with DevOps/CloudOps, combining automation with human expertise, and partnering with experts like Zymr, ensure enterprises stay resilient against evolving AI-driven and cloud-focused threats. Critical areas to focus on include evaluating firewalls, access controls, encryption methods, network segmentation, and patch management.
[PDF Version]
The National Authority for Cybersecurity received new advanced equipment to protect its network. This support strengthens Albania's cyber capacities. It marked an. Under the deal, Presight AI, a part of the G42 Group, will install surveillance cameras throughout Tirana and other major Albanian cities, as well as establish command and control centres. In a response to a Freedom of Information Act request, the Albanian Interior Ministry reported that the Smart. With the approval of Law No.
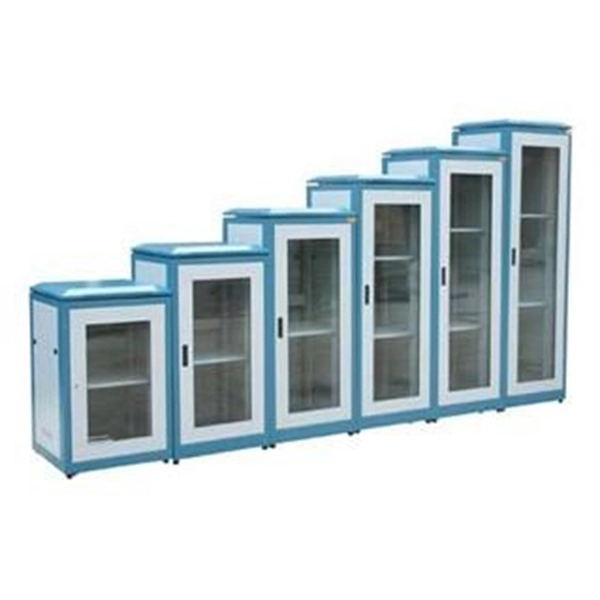
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. This guide evaluates the 10 best network security solutions for 2026, detailing technical specifications, key strengths, purchase rationale, and unique capabilities for global enterprises, mid-market growth companies, and hybrid workforces.
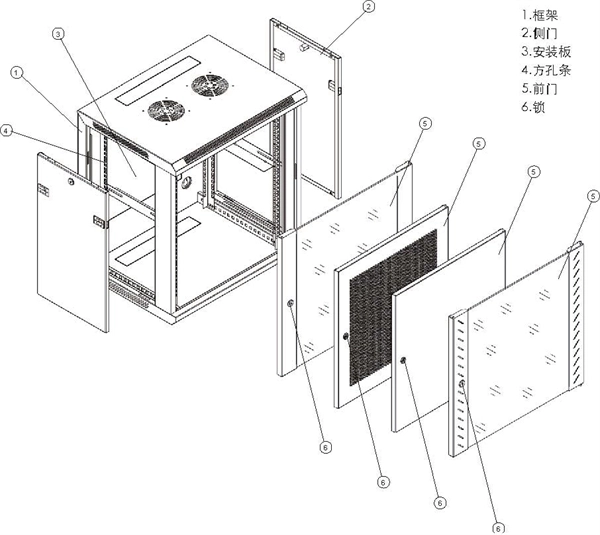
You'll get the precise, standardized dimensions of a 1U server rack unit — including height (1. 45 mm), width (19″ / 48. 26 cm), mounting hole spacing, and critical clearance allowances — plus actionable guidance on verifying physical fit, avoiding common installation. The IPC-C1E-BAR30-RH-N1 is an entry-level 1U appliance chassis with 15” depth for space-sensitive applications, such as Network & Security appliance, firewall, VPN, Telephony and military applications. 6” x 12”) motherboard can be populated into this appliance chassis. reserves the right to make any final modifications. For example, a typical full-size rack cage is 42U high, while equipment is typically 1U, 2U, 3U, or 4U high.
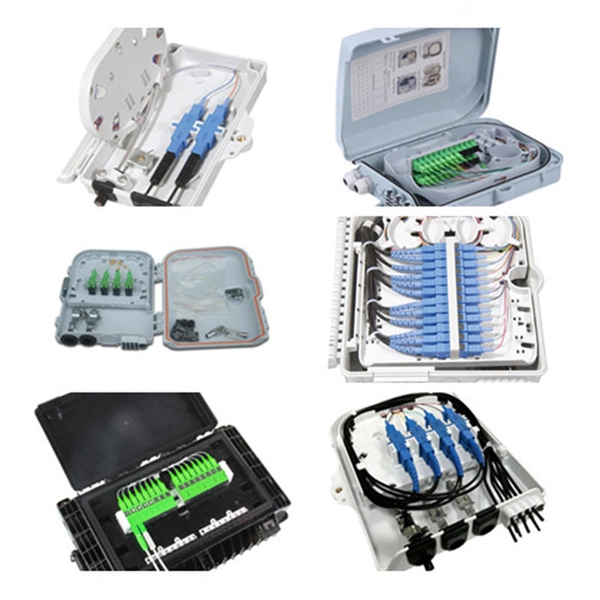
Key measures include securing network terminals, data centers, and access points with controlled entry systems, surveillance cameras, and fencing. Regular inspections and tamper-evident seals on fiber enclosures help detect unauthorized access or accidental damage early. Nowadays, the increasing reliance on fiber optic networks for transmitting vast amounts of data has brought about a pressing need for robust security measures to counter potential threats. In this fast-paced digital landscape, organizations must adopt a comprehensive approach to safeguarding their. In this blog, we will take an in-depth look at security measures for fiber optic communications, examining different strategies and technologies to ensure that data transmitted over this advanced infrastructure is intact and confidential. However, fiber is not invulnerable. Attackers with specialized tools can: Physically access unsecured junctions or cabinets.
[PDF Version]Contact us for competitive quotes on any of our power communication and smart grid products
Get a Quote